Designed for next-generation systems
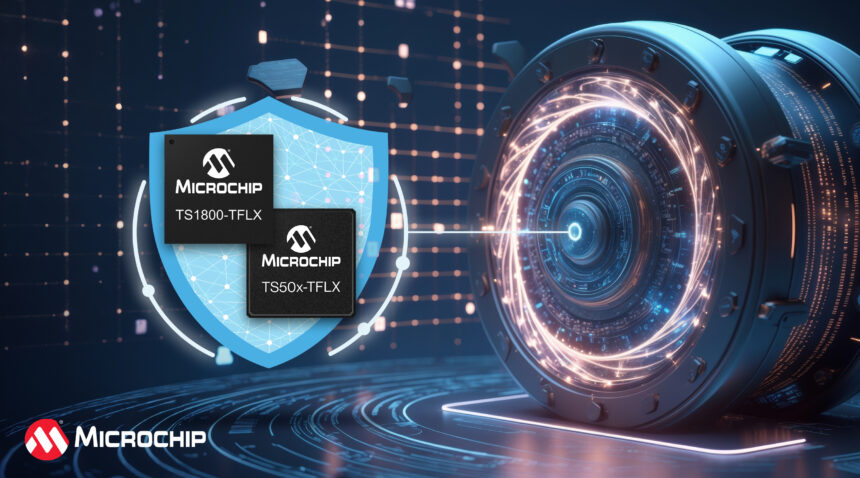
As the industry begins its transition to post-quantum cryptography (PQC), Microchip Technology is expanding its portfolio of Trust Shield, PQC-ready devices with the TS1800 Platform Root of Trust controller and the TS50x secure boot controller
The devices can help system architects address emerging cybersecurity mandates, including the European Cyber Resilience Act (CRA) and the Commercial National Security Algorithm Suite 2.0 (CNSA 2.0), while supporting data centre, compute, defence, telecommunication, and infrastructure security standards.
The TS1800 integrated circuit (IC) serves as an external Platform Root of Trust controller, facilitating secure boot, secure firmware updates, attestation and certificate handling using hardware-accelerated PQC. These accelerators implement National Institute of Standards and Technology (NIST) standardised algorithms such as ML-DSA, LMS verification, and ML-KEM.
Nuri Dagdeviren, corporate vice president of Microchip’s secure computing group, said, “The transition to post-quantum cryptography is no longer a discussion for the future; it’s a real-world implementation challenge already at our doorstep, arriving faster than many organisations expected. At Microchip, we’re helping customers address this implementation challenge by building PQC readiness directly into the foundation of system trust, so platforms can evolve securely as new threats and standards emerge.”
Developed around a high-performance Arm Cortex-M4F processor operating at up to 192NHz, the TS1800 provides up to twice the processing performance of previous generations of Microchip root-of-trust controllers, supporting the computational demands of PQC workloads.
Architectural enhancements and regulator optimisations maintain power efficiency and support advanced platform security functions needed for Open Compute Project (OCP)-compliant implementations, including secure boot, firmware integrity validation, attestation, and lifecycle management. Adding USB 2.0 reduces firmware update times compared to I²C and the Serial Peripheral Interface (SPI).
The TS50x family provides a PQC-secure boot solution for systems that do not need the full OCP-based Platform Root of Trust feature set. TS50x devices have a simpler architecture focused on verifying the operations of PQC and classic cryptography, such as Elliptic Curve Cryptography (ECC) P-384, for firmware booting from SPI Flash. These devices hold the main chipset on reset until the signature verification is successful, enabling companies to retrofit classic ECC cryptography with PQC.
The TS1800 and TS50x controllers support PQC and align with requirements such as NIST SP 800-193 platform resiliency guidelines and evolving security initiatives. The devices are available as part of the pre-configured TrustFlex platform to accelerate time-to-market. Developed as modular, drop-in crypto controllers, the devices can reduce the complexity and risk of upgrading cryptographic foundations across entire platforms.
By providing hardware-based PQC capabilities at the root of trust, the TS18000 and TS50x controllers support true PQC-based secure boot implementations that start at first power-on, instead of relying on software-based approaches that depend on classical cryptography for initial measurements. The devices expand on Microchip’s fourth-generation Soteria firmware, running on the Zephyr RTOS, to support evolving ecosystems and industry certification requirements.